How to use SSH keys to access your WordPress servers
SSH keys are an alternative to username and password combos. They are often used to access servers and they speed your life up, because you no longer need to remember a password to log in.
They can also be used to give multiple people access to a single account – for example the root account – whilst still having the ability to remove access for one user without removing access for the others. If you shared access to your root account with a username and password, to remove access to one person you would have to change the password, meaning everyone with legitimate access to that account would have to be told the new password.
What is SSH?
SSH stands for Secure Shell. A secure shell gives you command-line access to your server. SSH is a cryptographic networking protocol that lets you operate secure network services over an unsecured network. It is far more secure than a password alone and is not feasible to break with brute force.
The key thing to understand is that SSH keys exist in pairs, a public key and a private key. The public key you can share with anyone – for example you can place it in the right place on a server and you will be granted access without any passwords. The private key you guard with your life, or a password-protected folder will do.
They are really easy to generate, as this guide will show you.
Create your SSH key-pairs on a Mac
Open Terminal and create your SSH keys by running this command:
ssh-keygen -t rsaYou will get something that looks like this:
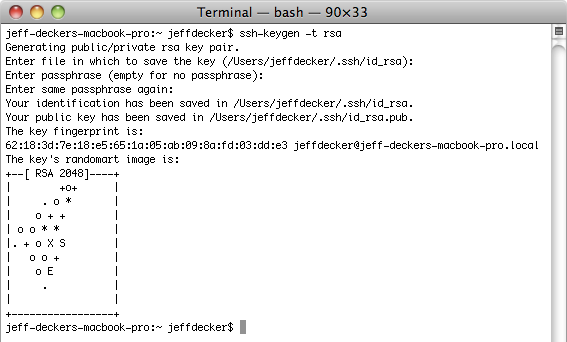
These days I generate an ed25519 key rather than RSA – ssh-keygen -t ed25519. It is shorter, faster and at least as secure. RSA is still perfectly fine if you already use it, but generate a 4096-bit key with ssh-keygen -t rsa -b 4096.
Storing and securing your keys on a Mac
On a Mac you will be asked where you want to store your keys. It will display the default location (i.e. home/user/xyz/.ssh/id_rsa.pub). You can put it where you want, but I would just press enter and get on with it.
You will then be offered the chance to add a password. This is up to you. I prefer securing the SSH keys folder within another encrypted, password-protected folder (how to on mac and windows). If you press enter again the keys will begin to generate and will be saved in the location previously specified. This is preferred because then you do not have to enter your password every time you connect. Also, some applications do not allow password-protected SSH keys.
The private key will be located in: home/user/xyz/.ssh/id_rsa
The public key will be here: home/user/xyz/.ssh/id_rsa.pub
Create your SSH keys on Windows
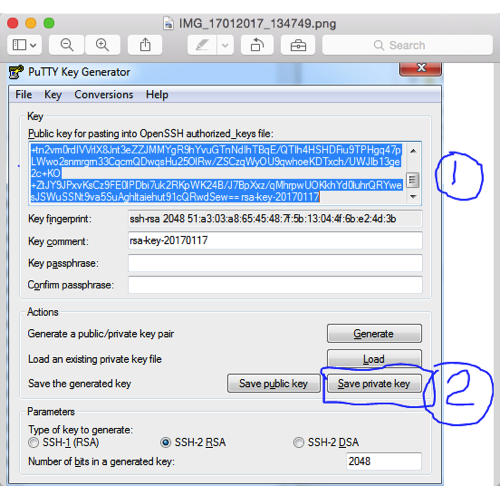
Windows 10 and Windows 11 now ship with the OpenSSH client built in, so you can run ssh-keygen and ssh straight from PowerShell or Windows Terminal exactly as you would on a Mac. PuTTY and its PuTTYgen tool still work well if you prefer a graphical approach:
- Launch the PuTTYgen program, then click the Generate button. The program generates the keys for you.
- Enter a unique key passphrase in the Key passphrase and Confirm passphrase fields.
- Copy the public key ready for adding to your server (marked 1 below), then click save on both the public and private keys and pick somewhere secure to store them.
Storing and securing your keys on Windows
I would recommend using the same method as described on Mac, storing them password-less within an encrypted folder. You can find a guide to do that here: Microsoft: how to encrypt a file.
Adding SSH keys to your server
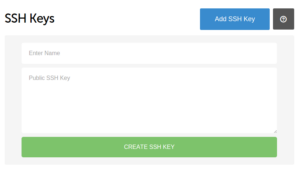
If you are using Digital Ocean, you can add your SSH key when you create a new droplet. Just paste your public key into the box they provide. Our guide to creating a Digital Ocean droplet for the Rocket stack walks through the whole process.
If you already have a server with a username and password combo, you need to log onto it with PuTTY, Terminal or FileZilla and modify the following file:
/root/.ssh/authorized_keysIn that file there is one public key per row. If it is empty, just paste your public key in there. If there are already other keys, add a new line and paste your public key. Now you will be able to access your server using SSH.
Once key-based login is working, disable password authentication in /etc/ssh/sshd_config (set PasswordAuthentication no and reload sshd). Brute-force password attacks then have nothing to guess against. See our complete guide to WordPress security for the wider hardening picture.
Access your server using SSH keys on a Mac
Open Terminal and run the following command:
ssh root@yourserveripaddressYou will be confronted with a message along the lines of:
The authenticity of host 'an ip address here (same ip address here)' can't be established.
ED25519 key fingerprint is: public key fingerprint will be here.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added 'ip address' (ED25519) to the list of known hosts.
Nothing to worry about. Just check and confirm the IP address is correct and press enter.
Access your server using SSH keys on Windows
When you open PuTTY the configuration window should appear:
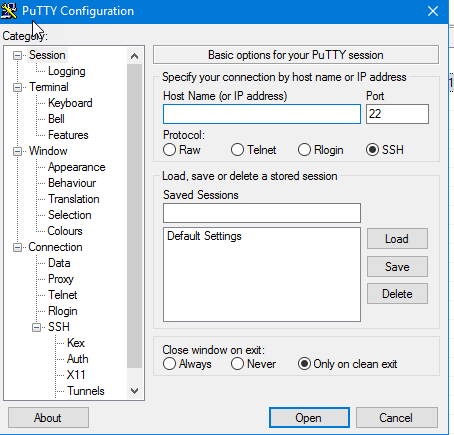
You simply enter the IP address into the field marked “Host Name (or IP address)” and click open or press enter.
A box like this should appear:
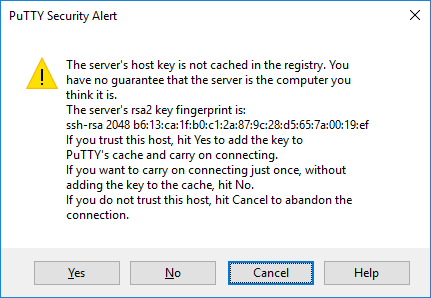
Click yes and you will be connected.
Removing SSH keys
That is all there is to it. If you want to grant access to other people, you can just open up that /root/.ssh/authorized_keys file and add their public key. Remove the line when you need to remove their access.
Digital Ocean’s community tutorials are also a lot of help.

Comments